Spending Signatures Directing Upgrades in Encrypted Mobile Exchange Platforms
Written by Clara Beck · Aug 29, 2026
Spending Signatures Directing Upgrades in Encrypted Mobile Exchange Platforms
Transaction records in portable exchange services generate detailed spending signatures that reveal usage trends without exposing individual identities, and these signatures now guide targeted capability enhancements in encrypted environments. Developers examine aggregated data streams to identify where users encounter friction during transfers or authentication steps, then refine algorithms that maintain encryption standards across all operations.
Pattern Recognition in Secure Data Flows
Encrypted portable exchange platforms process millions of daily interactions, yet the underlying signatures emerge from combined metrics such as frequency of method selections, average transfer sizes, adn timing sequences during peak hours. Research indicates that these aggregated patterns allow teams to prioritize features like streamlined verification flows or expanded support for specific currency pairs, all while preserving end-to-end encryption protocols. According to reports from the European Data Protection Board, such analysis stays within regulatory boundaries that prohibit direct access to personal identifiers.
One study conducted across multiple regions showed that platforms incorporating signature-based adjustments reduced failed transaction rates by measurable margins between 2024 and 2025, and similar refinements continued into August 2026 as new encryption layers rolled out in response to observed behavioral clusters. Observers note that these updates focus on areas where spending signatures indicate repeated authentication delays, prompting additions such as biometric fallback options or pre-validated device pairings that operate without compromising cryptographic safeguards.
Encryption Standards and Adaptive Enhancements
Modern portable exchange services rely on layered encryption that protects both stored records and live transaction data, and spending signatures supply the directional cues for where to allocate development resources. Engineers review anonymized logs to detect patterns linked to particular device types or network conditions, then implement capability upgrades that strengthen resilience against emerging threats. Data from the Australian Competition and Consumer Commission highlights how regulatory frameworks encourage this form of iterative improvement, provided that all enhancements maintain strict separation between analytical processes and user identities.
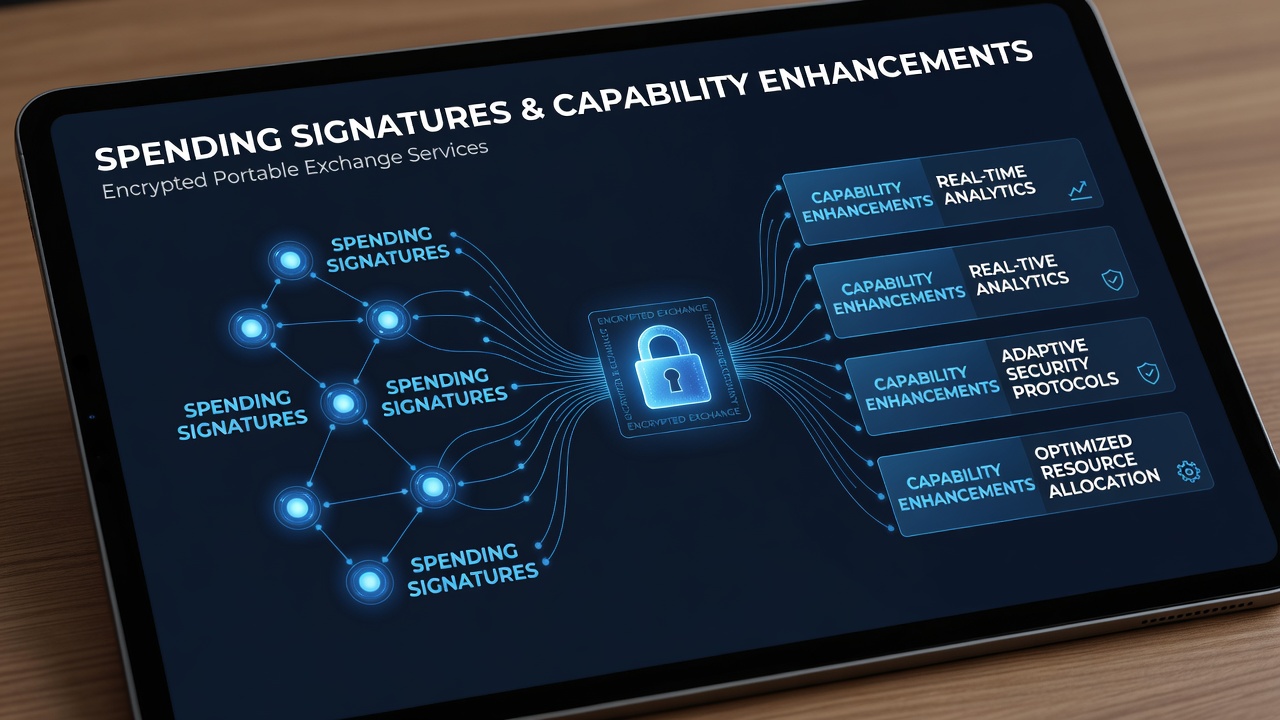
Platforms that integrate these insights have introduced features such as dynamic limit adjustments and real-time anomaly detection modules, each calibrated against historical signature clusters. Researchers at several academic institutions have documented how these targeted changes improve overall system efficiency without requiring broader data exposure, and the process relies on continuous feedback loops that remain fully contained within encrypted boundaries. What's interesting is the way certain signatures tied to cross-border transfers have prompted the addition of localized compliance checks that activate automatically during high-volume periods.
Regulatory Alignment Across Jurisdictions
Global standards for data protection shape how spending signatures inform platform development, with organizations like the Office of the Privacy Commissioner of Canada and various national bodies setting expectations for transparency in algorithmic decision-making. These frameworks require that any capability enhancements derived from pattern analysis undergo independent review to confirm they do not inadvertently reveal individual details. Evidence suggests that services operating under multiple regulatory regimes coordinate their upgrades to satisfy overlapping requirements, resulting in more uniform security postures across regions.
By August 2026, several major platforms had aligned their enhancement schedules with updated guidelines issued by the U.S. Federal Trade Commission, incorporating signature-driven refinements into core encryption modules. Those who've examined the resulting systems report that the changes maintain user method selections and account configurations in protected states while allowing operational improvements based on collective usage data. The reality is that such alignment reduces the risk of compliance gaps that could otherwise stall feature deployments.
Future Trajectories for Signature-Guided Systems
Continued evolution in encrypted portable exchange services will likely center on increasingly granular spending signatures that account for emerging transaction types and device ecosystems. Industry reports from organizations such as the International Association of Privacy Professionals point to ongoing work that refines how these patterns translate into specific technical upgrades, always under the constraint of unbreakable encryption. Academic papers from European universities have begun modeling scenarios where signature analysis predicts infrastructure needs months ahead, enabling proactive rather than reactive enhancements.
Conclusion
Spending signatures continue to serve as reliable indicators for directing capability enhancements within encrypted portable exchange services, and the process integrates regulatory expectations from multiple jurisdictions while preserving core privacy protections. Platforms that leverage these patterns achieve measurable improvements in transaction reliability and feature relevance, all documented through objective data collection methods that exclude personal exposure. As developments progress past August 2026, the same principles are expected to underpin further refinements across the sector.